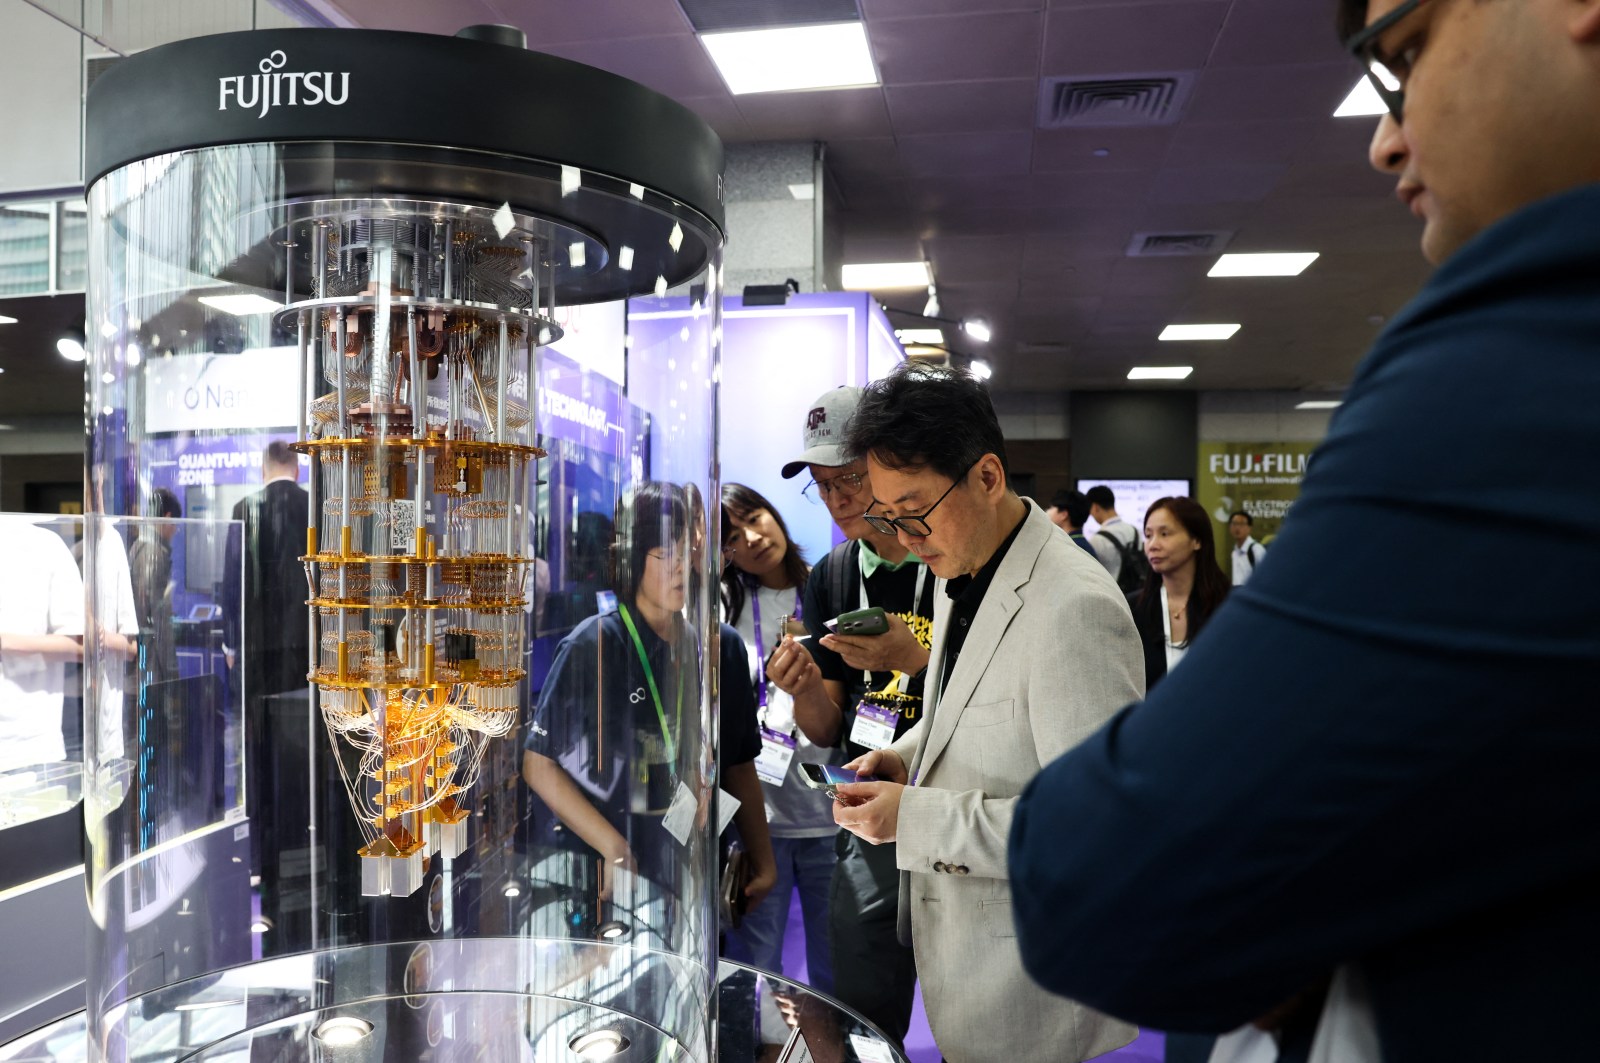
Quantum security has become an urgent consideration for infrastructure planning. Previously, companies viewed quantum risk as a distant concern, relevant for the future but not immediate enough to influence current infrastructure decisions. This stance is increasingly untenable. Banks, payment companies, cloud providers, and digital asset platforms rely on cryptography to secure various aspects, including money, identity, and communications. If the cryptographic systems they depend on need modification, the process will be long, complex, and operationally challenging. It is wise to begin preparations early.
The Threat of Quantum Computing
The concern around quantum computing is clear. Quantum computers with sufficient power may compromise many of today’s public-key cryptographic systems. These systems secure digital signatures, encrypted communications, identity frameworks, and financial transactions. Organizations safeguarding high-value assets must prepare by transitioning to quantum-safe encryption methods, a challenging task.
One complication is the unclear path to achieving quantum security. Although standards are developing, many practical implementation issues remain unresolved. This uncertainty might tempt company leaders to delay addressing quantum security, but that would be a significant error. Companies investing in quantum security now gain a crucial advantage in managing what could be among the most complex infrastructure migrations of the coming decade.
Understanding Cryptographic Dependencies
Most large organizations lack a comprehensive map of where cryptography exists within their infrastructure, creating a serious issue. To make a system quantum secure, a full understanding of the system’s workings is essential. Companies should identify elements like signature schemes, encryption systems, key management flows, authentication mechanisms, vendor dependencies, cloud services, and legacy systems. Although this might sound basic, it is often complex due to years of software, vendor integrations, and workarounds.
Organizations starting early can address critical questions. Which systems use algorithms vulnerable in a quantum future? Which keys safeguard high-value or long-term sensitive data? Which vendors introduce downstream vulnerabilities? Knowing these details allows companies to prioritize and manage quantum migration without treating it as one massive task.
Testing and Development Needs
The U.S. National Institute of Standards and Technology (NIST) has been pivotal in this transition, evaluating and standardizing post-quantum cryptographic algorithms. For financial institutions, cloud providers, and infrastructure companies, NIST provides a benchmark for credible algorithms suitable for testing. However, standards alone do not equate to readied infrastructure. Institutions still need to grasp how quantum-safe signatures and encryption function within actual systems.
These entities should test these algorithms under critical operational conditions, such as transaction size, latency, cost, key management, and resilience. The questions are vital for institutions using distributed signing and multi-party computation (MPC)-based custody, as this model protects against single points of failure and supports distributed approval workflows. Implementing post-quantum signatures must align with these models and be tested through practical experimentation.
Gradual Migration and Customer Assurance
Early starters can increment their migration rather than rush it. Security migrations typically require extensive testing, audits, compatibility checks, and stakeholder communication. By initiating early, companies can run pilots, assess tradeoffs in hybrid systems, and phase upgrades into ongoing operations. Many companies might run classical and post-quantum systems concurrently to test new protections while maintaining current security bases.
Delayed action might force companies to replace key infrastructure in crisis situations. Institutions that cannot afford downtime or uncertain key management should be particularly careful about waiting too long. Customers and partners consider security in their due diligence processes. Quantum risk will add to this scrutiny because it impacts crucial systems such as identity and transaction approval. Companies unable to demonstrate a quantum-readiness plan may appear less prepared.
Shaping Market Standards and Institutional Action
Organizations that begin experimenting with quantum security can help set market standards. These early adopters influence expectations around timelines, hybrid deployment, custody, signing architecture, and risk governance. Institutions such as HSBC and JPMorgan Chase are already testing quantum-secure infrastructure in valuable contexts. Examples include HSBC trialing technology for tokenized physical gold and JPMorgan Chase developing quantum-safe digital signature capabilities.
These initiatives, although early, point to a broader shift where quantum security becomes a tangible, rather than theoretical, challenge. Companies advancing their understanding now gain a capability edge in future infrastructure evolution.
Leave a Reply